
The specific, unglamorous details ofhow your data stays safe.
You're trusting us with the data behind real settlement and revenue. This page documents exactly what we do to earn that, and where we're honest that we're not finished yet.
Every credential and every record is scoped to your tenant, encrypted, and traceable back to the person who touched it, by design, not by policy alone.
Your data doesn't have to leave your infrastructure.That's not a feature, it's your choice to make.
If data residency is a hard requirement, not a preference, Seam can run entirely inside your own environment. Same reconciliation, settlement, and profitability engines. Nothing transmitted to us unless you choose to.
Scoped by design,not by discipline.
A permission isn't a setting someone remembered to switch on. Every request carries the tenant it belongs to and the role that made it, and the log of that is written where the application can't edit it.
Per Tenant Isolation
Every institution's data sits in its own isolated tenant boundary. Access checks happen at the connection level, not left to a query to get right every time.
Read-Only By Default
Where Seam connects to your own database, it connects with read-only credentials. We have no write path into your source systems, even if we wanted one.
Role Based Permissions
Not every teammate needs to touch every module. Sensitive actions, like credential management and cost configuration, are scoped by role.
Audit Log on Sensitive Actions
Credential changes, configuration changes and data exports are logged with who, what and when, and that log isn't editable from inside the application.
Encrypted in transit,encrypted at rest.
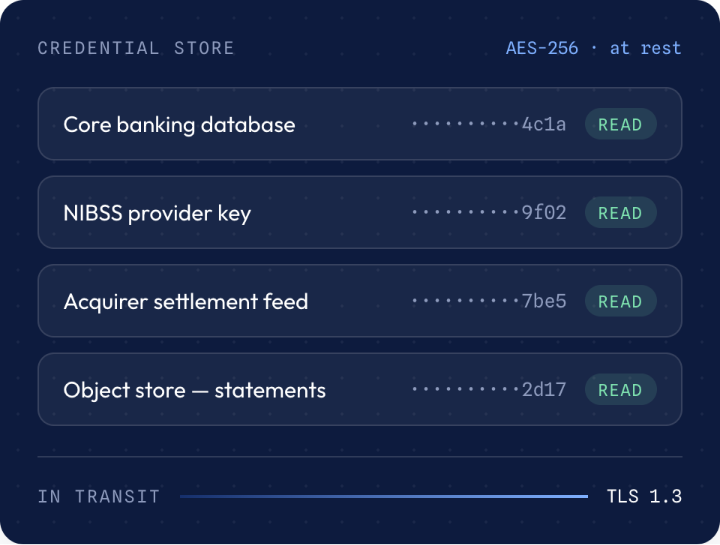
Credentials never sit next to the records they unlock. They live in their own access-controlled store, encrypted, and the application holds a reference, not the secret.
Encryption in Transit
Every connection, browser to platform, platform to your connected sources, runs over TLS. Nothing moves between systems unencrypted.
Encryption at Rest
Stored credentials and sensitive configuration are encrypted at rest, separate from the application layer that uses them.
Credentials Isolated
Provider and connection credentials live in a dedicated, access-controlled store, not alongside general application data.
Deployment Flexibility
API, on your own infrastructure, or engines-only with your own database. How much of your data ever leaves your environment is your choice, not ours.
Some of the above is described at the level of practice we hold ourselves to today, ahead of the third-party audit that will let us state it more precisely, see Compliance Status below for exactly where each certification stands.
What we're built tonever touch.
Out of Scope
Card numbers (PAN), CVV, or card expiry data
Customer BVN or full bank account credentials
Payment authorisation tokens capable of initiating a transaction
End-user passwords from your own systems
What Seam Actually Handles
Settled transaction metadata: amount, reference, date, status
Reconciliation and settlement records already visible in your own systems
Configuration for cost, rules, and matching logic you define
Read-only connections to the sources you explicitly connect
Where we actually stand,stated plainly.
We're an early-stage platform and would rather tell you exactly where we stand than round up. If a certification is a hard requirement for your evaluation, talk to us directly about timeline and options.
IN PROGRESS- TARGETING 2027
NDPR (Nigeria)
Integrate Seam's APIs directly into your own stack, systems or ERPs. Seam becomes another service your existing infrastructure calls.
PLANNED 2027
ISO 27001
Have the full platform deployed on infrastructure you control. Same product, same modules running where your data already lives.
NOT IN SCOPE
PCI DSS
Use Seam's reconciliation, settlement and profitability engines while keeping your data in a database you own and control.
We're an early-stage platform and would rather tell you exactly where we stand than round up. If a certification is a hard requirement for your evaluation, talk to us directly about timeline and options.
Security starts with where yourdata actually lives.
API Integration
Seam's APIs sit inside your own stack. You control the perimeter; we control the logic.
Platform, On Your Infrastructure
The full platform, deployed where your data already lives, for institutions with strict data-residency requirements.
Engines only, BYOD
Use Seam's reconciliation and profitability logic while your data stays in a database you own and control.
If you find a security issue, we want to hear about it before anyone else does. Email us with details, we acknowledge every report and treat high-severity findings as a priority.